Penetration testing powered by real hackers, governed like a service. No automation noise. Pure creativity.

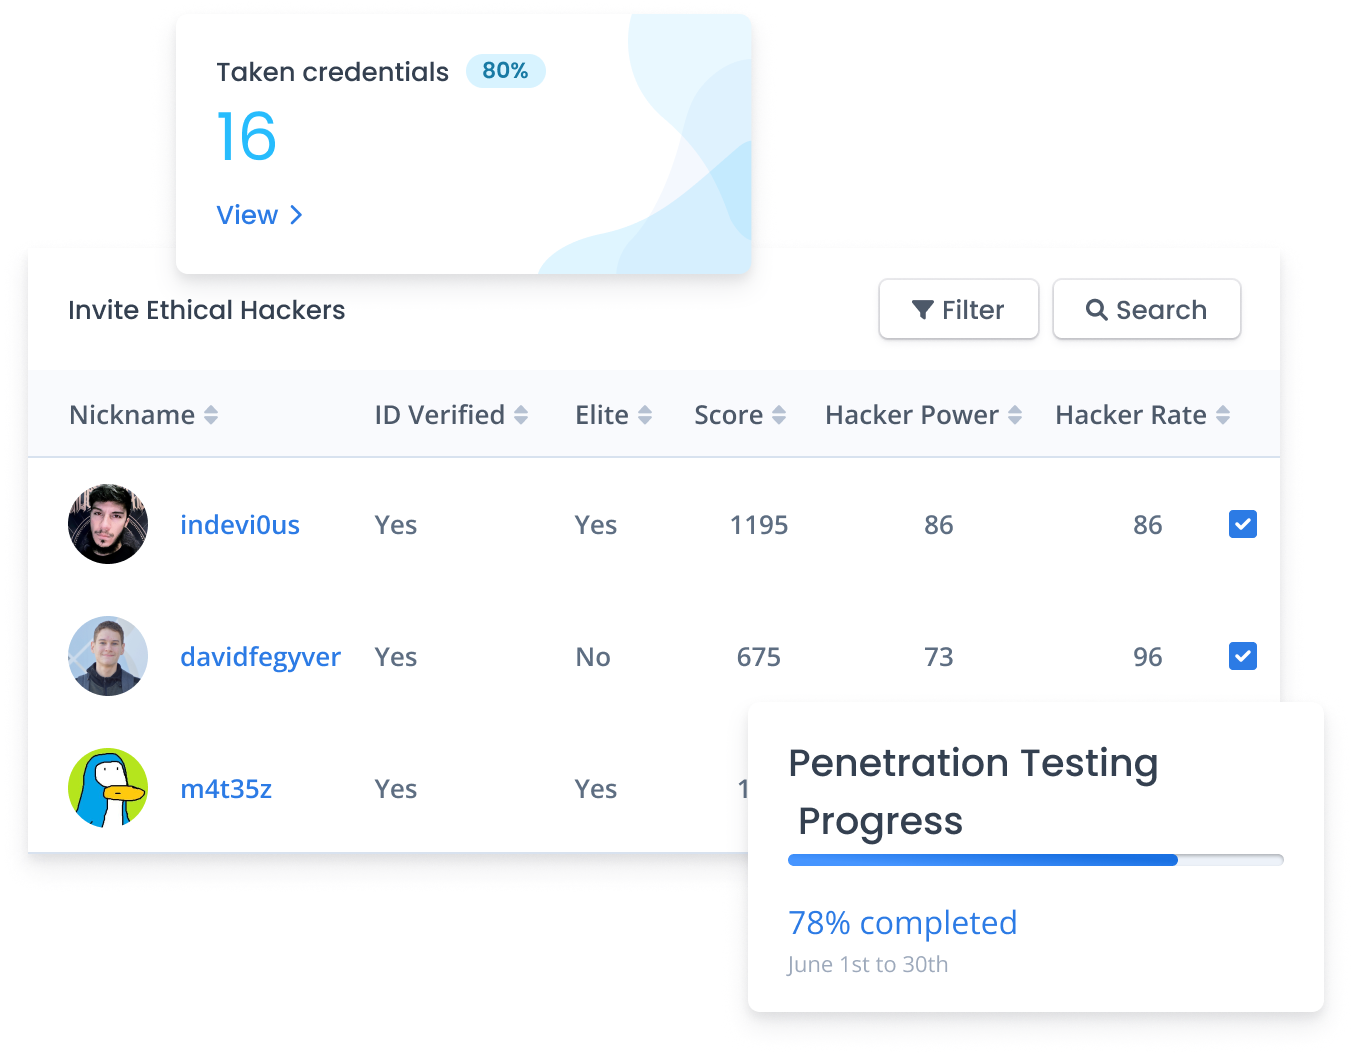
Penetration testing dashboard for inviting ethical hackers and tracking progress

From scope to impact, in days - not months.

The expertise of 5 - 20, delivered at the cost of 1.

Scale your security team instantly - without hiring.

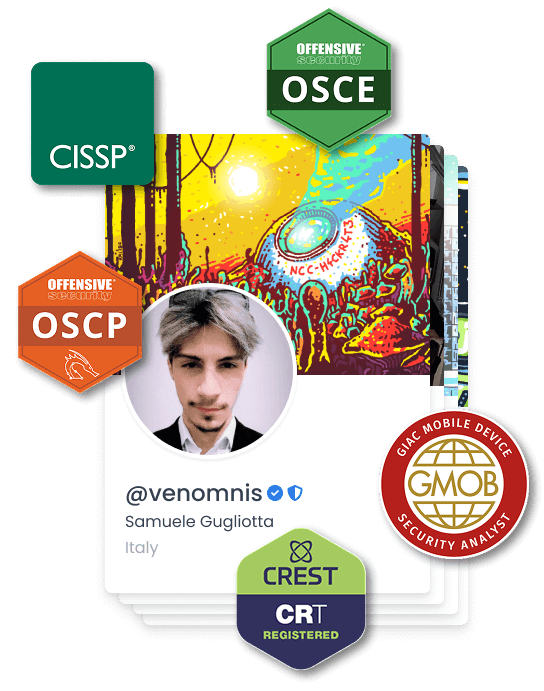
Verified ethical hacker profile with OSCP, OSCE, CISSP, GMOB and CRT certifications

{Why Pentest as a Service?}

In-depth assessment

The global community of motivated, ethical hackers with a more diverse skillset can provide much better results than traditional pentests. Our ethical hackers hold industry-recognized certifications such as OSCP, OSCE, CISSP, and CEH.

Flexibility

With Pentest as a Service, you can choose from a great variety of testing services, from a web app and mobile app testing to API testing. Our team gives you support during the planning process and we make sure that the testing can start within a few days.

Real-time visibility

Access reported vulnerabilities immediately via our platform. We help determine the severity of bugs and make sure you only receive accurate reports. With Hackrate, you can keep vulnerability reports centralized and easy to manage.

Ticketing system integration

With our platform, the reported vulnerabilities can be easily added to ticketing systems like Jira Cloud.

Ensure compliance

By testing your security capabilities regularly, we help you comply with security standards and regulations.

Verified Hackers

To provide a group of selected and verified ethical hackers, we are using KYC verification services.

Designed to support SOC 2 / ISO 27001 programs

SOC 2 compliance standard
ISO 27001 information security standard
PCI DSS payment card security standard
HIPAA healthcare data protection standard
GDPR data protection regulation
NIS2 cybersecurity directive

Compliance-ready deliverables

Crowdsourced security testing provides a unique method to find your weaknesses and be more secure.

Effective: Our service can be at least two times more cost-effective than hiring external security research to identify vulnerabilities.

Confidential: The security testing is an "invitation-only" type of service. Testing is only accessible to a selected group of hackers (usually 4-10 ethical hackers).

Fast: The suggested length of the security testing is one month, but the first vulnerabilities are usually found within the first few hours.

Test your application, API, or network for any security vulnerabilities. You can choose from a great variety of testing services:

Web application - Identify vulnerabilities in web applications.

Mobile application - Test your mobile assets (iOS and Android devices)

API - Find security vulnerabilities in your API.

Network - Test your network environment.

Other - Test for vulnerabilities in blockchain, IoT devices, or desktop applications.
Real-World Attack Coverage

Ethical hackers think like attackers - not scanners.

The result:
Issues that matter, not just issues that exist.
Logic flaws

Broken workflows, missing checks, and edge cases that scanners don’t understand.

Business-impact vulnerabilities

Findings tied to revenue, fraud, data exposure, and operational risk.

Chained & creative attack paths

Real exploitation sequences across features, roles, and systems.

Built for real-world adversaries, not checkbox security.
Enterprise-Ready Reporting

Reports that auditors and executives can actually use.

Clear structure, consistent severity, and documentation that stands up to scrutiny — without burying teams in noise.

Suitable for
ISO 27001, SOC 2, internal audits, and executive reporting.
  • 1
    Structured vulnerability reports
    Consistent format: impact, evidence, reproduction steps, and remediation guidance.
  • 2
    Severity-based prioritization
    Triage that maps to business risk so teams know what to fix first.
  • 3
    Audit-ready documentation
    Evidence trails and summaries that support compliance reviews and leadership reporting.
ISO 27001 SOC 2 Internal Audit Executive-ready

Learn more about Pentest as a Service

Want to know more about Pentest as a Service? Download our detailed datasheet today to find out how to manage your security tests and be sure that your company is secure.

Choose the right model

Three ways to run penetration testing with Hackrate.

Select a focused internal assessment, an invitation-only crowdsourced engagement, or a coordinated annual program.

  Traditional Pentest Crowdsourced Pentest Continuous Pentest
Engagement model One scoped assessment One scoped, invitation-only assessment Recurring 12-month program
Testing team Hackrate internal team only Selected Elite Ethical Hackers Internal team, Elite Ethical Hackers, or a hybrid
Best suited for Sensitive, restricted, or traditional assessment requirements Creative testing with diverse attacker perspectives Enterprise teams with multiple targets and recurring needs
Customer control Customer approves scope and internal access Customer approves scope and selected-hacker participation Customer approves the model for every target
Results PDF only or platform plus PDF Hackrate platform and agreed reporting Centralized platform results across the annual program
Planning Project scoping before the assessment Project scoping before the assessment Annual roadmap and monthly prioritization
Explore Explore Traditional Pentest Explore Crowdsourced Pentest Explore Continuous Pentest
Focused assessment

Traditional Pentest

Engagement
One scoped assessment
Testing team
Hackrate internal team only
Best suited for
Sensitive, restricted, or traditional assessment requirements
Customer control
Customer approves scope and internal access
Results
PDF only or platform plus PDF
Planning
Project scoping before the assessment
Explore Traditional Pentest
Diverse perspectives

Crowdsourced Pentest

Engagement
One scoped, invitation-only assessment
Testing team
Selected Elite Ethical Hackers
Best suited for
Creative testing with diverse attacker perspectives
Customer control
Customer approves scope and selected-hacker participation
Results
Hackrate platform and agreed reporting
Planning
Project scoping before the assessment
Explore Crowdsourced Pentest
Ongoing program

Continuous Pentest

Engagement
Recurring 12-month program
Testing team
Internal team, Elite Ethical Hackers, or a hybrid
Best suited for
Enterprise teams with multiple targets and recurring needs
Customer control
Customer approves the model for every target
Results
Centralized platform results across the annual program
Planning
Annual roadmap and monthly prioritization
Explore Continuous Pentest

Put expert hackers on your highest-risk targets

Turn your next pentest into faster security progress.

Define the scope, engage selected ethical hackers, and manage validated findings through one coordinated platform from testing to remediation.

Discuss Your PTaaS Scope
Hackrate

Our platform helps companies to identify software vulnerabilities in a cost-efficient way. It provides a secure and centralized view of ethical hacking projects for your company.

US Patent Applied for HackGATE #63/645,845

Checking service status...

Hackrate Ethical Hacking Platform |
2026 ©

CVE Program Numbering Authority