BUG BOUNTY PROGRAM
Bug Bounty
Program.
A bug bounty is about using the power of crowdsourced security to protect your business. During a bug bounty program, a company can offer rewards to ethical hackers for reporting vulnerabilities.
From discovery to resolution
{Main benefits}
The bug bounty program is a proactive way to secure your business.
Hackrate can help you go beyond textbook testing methods and find hidden vulnerabilities. Our creative ethical hackers simulate real-world attacks to get accurate results and identify gaps that can lead to a data breach.
Continuous testing
Penetration tests are time-bound activities, but with a bug bounty program, you can achieve continuous security testing of your product changes. Our experienced ethical hackers are using the latest tools to reveal security holes effectively.
Increase the trust
Prevent potential data breaches by reducing security risks. With Hackrate, you can create a culture of transparency and responsibility by actively improving your security level, which means a strong commitment to security.
Centralized view
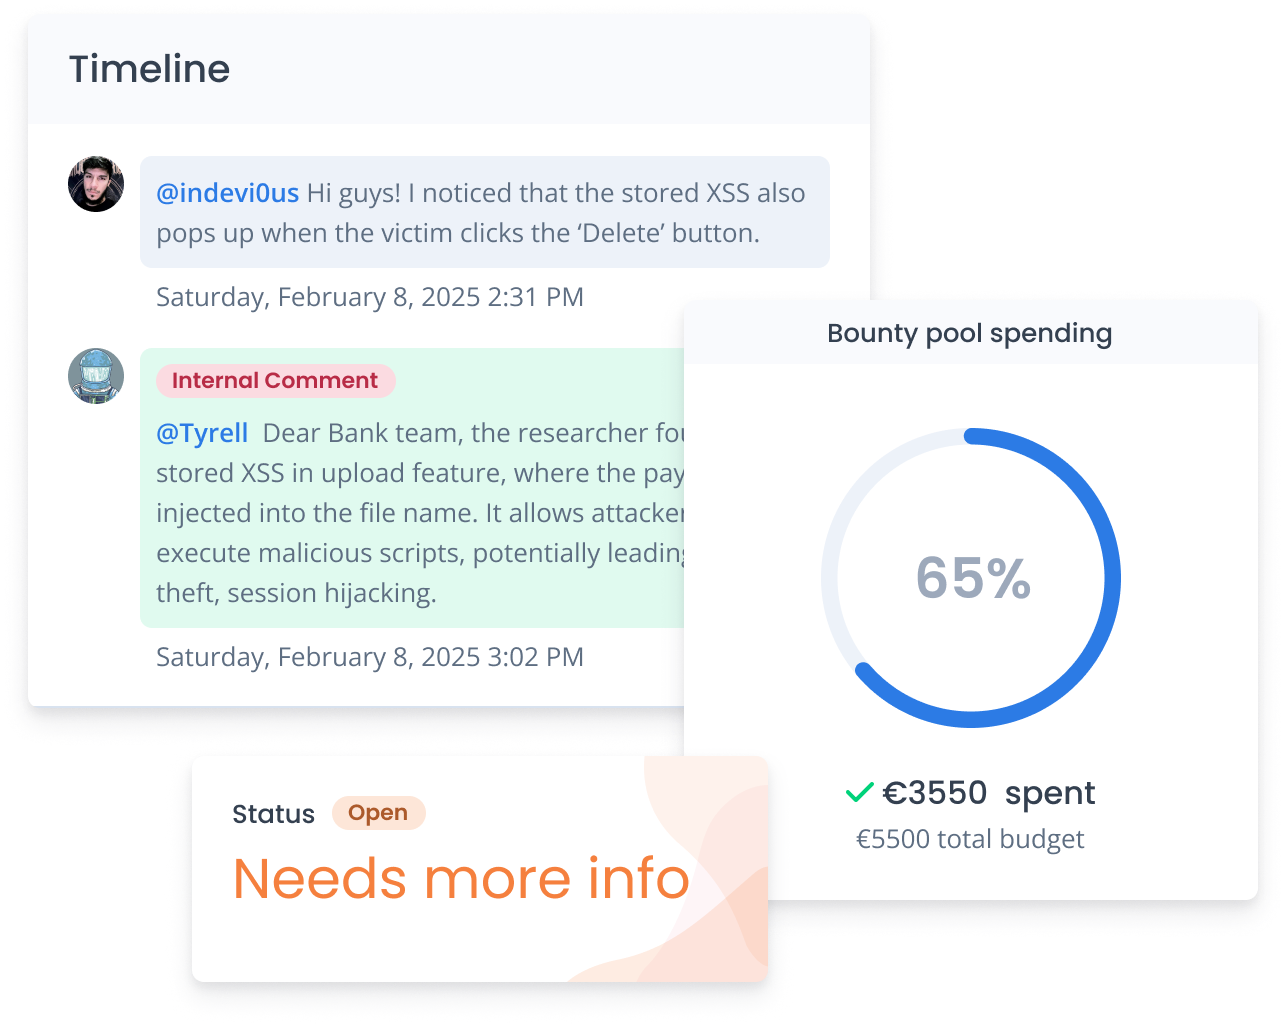
Our secure platform helps keep vulnerability reports centralized and easy to manage, while giving you immediate access to identified security vulnerabilities. Our built-in dashboard also allows you to track the bug bounty budget.
HUMAN EXPERTISE
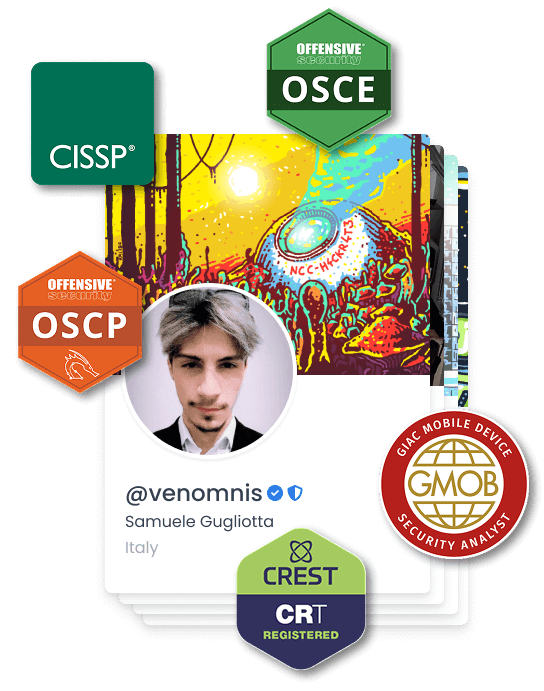
Work with the global ethical hacking community
Multiply your security capabilities, not your headcount.
ACTIONABLE FINDINGS
Fast, validated, and ready to fix.
FLEXIBLE PROGRAM MODELS
Built to match your maturity
Start focused, then expand - without switching platforms.
Outcome: Your bug bounty grows with you.
Invite-only
High-signal testing with vetted hackers.
Ongoing programs
Always-on coverage as you ship.
Alongside pentesting
Combine deep tests with crowd creativity.
Gradual rollout
From small scope to full coverage.
Explore bug bounty program types
FROM SCOPE TO REMEDIATION
Bug bounty program in four steps
Definition of the scope
Definition of the objectives and requirements, especially what is in the scope, what are the rewards for the reported vulnerabilities, and the number of hackers invited to the program. Our experienced team tailors the program exactly to your needs. We can keep your programs private (with selected ethical hackers) or make your program public (open to our ethical hacker community).
Preparation for testing
Finalization of the testing plan, which contains the timeline and the bug bounty program's rules. For example, it must specify what hackers can and cannot do during testing and which kinds of vulnerabilities are accepted. Our team helps you prepare and find the best security testing strategy for your needs.
Testing and reporting
Hackrate launches the program and invites ethical hackers. During the testing, ethical hackers submit bug reports with details on how to exploit the bug. Communication is key in maintaining trust during the process. Our team helps with the communication and verifies the bugs reported by the ethical hackers. Your company receives updates on submitted vulnerabilities immediately via our platform.
Remediation of risks
After the validation of reports submitted through our platform, you can start the resolution of identified risks with the help of hackers. With realistic tests of your system's defenses, you will be able to prioritize the vulnerabilities discovered during the tests. Ethical hackers get rewards and reputation points on our platform based on the severity of the identified vulnerabilities.
REAL-WORLD ATTACK COVERAGE
Ethical hackers think like attackers - not scanners.
The result: Issues that matter, not just issues that exist.
Logic flaws
Broken workflows, missing checks, and edge cases that scanners don’t understand.
Business-impact vulnerabilities
Findings tied to revenue, fraud, data exposure, and operational risk.
Chained & creative attack paths
Real exploitation sequences across features, roles, and systems.
Built for real-world adversaries, not checkbox security.
ENTERPRISE-READY REPORTING
Reports that auditors and executives can actually use.
Clear structure, consistent severity, and documentation that stands up to scrutiny - without burying teams in noise.
ISO 27001, SOC 2, internal audits, and executive reporting.
- 01
Structured vulnerability reports
Consistent format: impact, evidence, reproduction steps, and remediation guidance.
- 02
Severity-based prioritization
Triage that maps to business risk so teams know what to fix first.
- 03
Audit-ready documentation
Evidence trails and summaries that support compliance reviews and leadership reporting.
THE BUG BOUNTY DATASHEET
Learn more about Bug Bounty Program
Want to know more about Bug Bounty? Download our detailed datasheet today to find out how to proactively secure your business with our Bug Bounty Program.
BUG BOUNTY PROGRAM / DATASHEET
RECOGNIZED EXPERTISE
Proven expertise, recognized by industry leaders.

Hackrate bounty hunters have earned Hall of Fame acknowledgements from some of the world’s most respected technology and financial organizations.
Bug Bounty without suprises
Human creativity. Clear rules.
Full control.
If you want the benefits of the hacker community - without the operational risk - Hackrate’s Bug Bounty programs are built for you.
PLAN YOUR NEXT STEP
Practical guides. Clearer decisions.
Explore the people, preparation and choices behind a working researcher program.
Expert Answers from Levente Molnár
Hackrate CTO Levente Molnár explains bug bounty and managed VDP decisions: team workload, researcher selection, critical reports and getting started.
Read the guideHow Much Time Will Our Team Need?
See the customer tasks behind managed bug bounty and VDP programs: scope, technical access, risk decisions, remediation and urgent escalation.
Read the guideBug Bounty Without an Internal Security Team
Run a managed bug bounty without a dedicated security team. Understand customer ownership, engineering readiness, validation support and VDP alternatives.
Read the guideYour First Month with Hackrate
Explore an illustrative first month of managed bug bounty or VDP: objectives, scope, preparation, launch readiness, report handling and program review.
Read the guideTurn hacker creativity into controlled coverage
Launch a bug bounty program built around your risk.
Define the scope, rules, and rewards. Hackrate coordinates ethical hackers, validates incoming reports, and helps your team focus on vulnerabilities that matter.

Hackrate
Our platform helps companies to identify software vulnerabilities in a cost-efficient way. It provides a secure and centralized view of ethical hacking projects for your company.
US Patent Applied for HackGATE #63/645,845
Products
From the Blog
-
Hackrate Ranked 1st in Hungary and 22nd Globally at Hack The Box’s Global Cyber Skills Benchmark 2026
May 29 • 13 min read
-
Press release: Hackrate becomes Hungary’s first CVE Numbering Authority
Jan 13 • 5 min read ★
-
Let 2026 be the year bug bounty becomes part of how you build and operate
Jan 05 • 4 min read
 Numbering Authority